
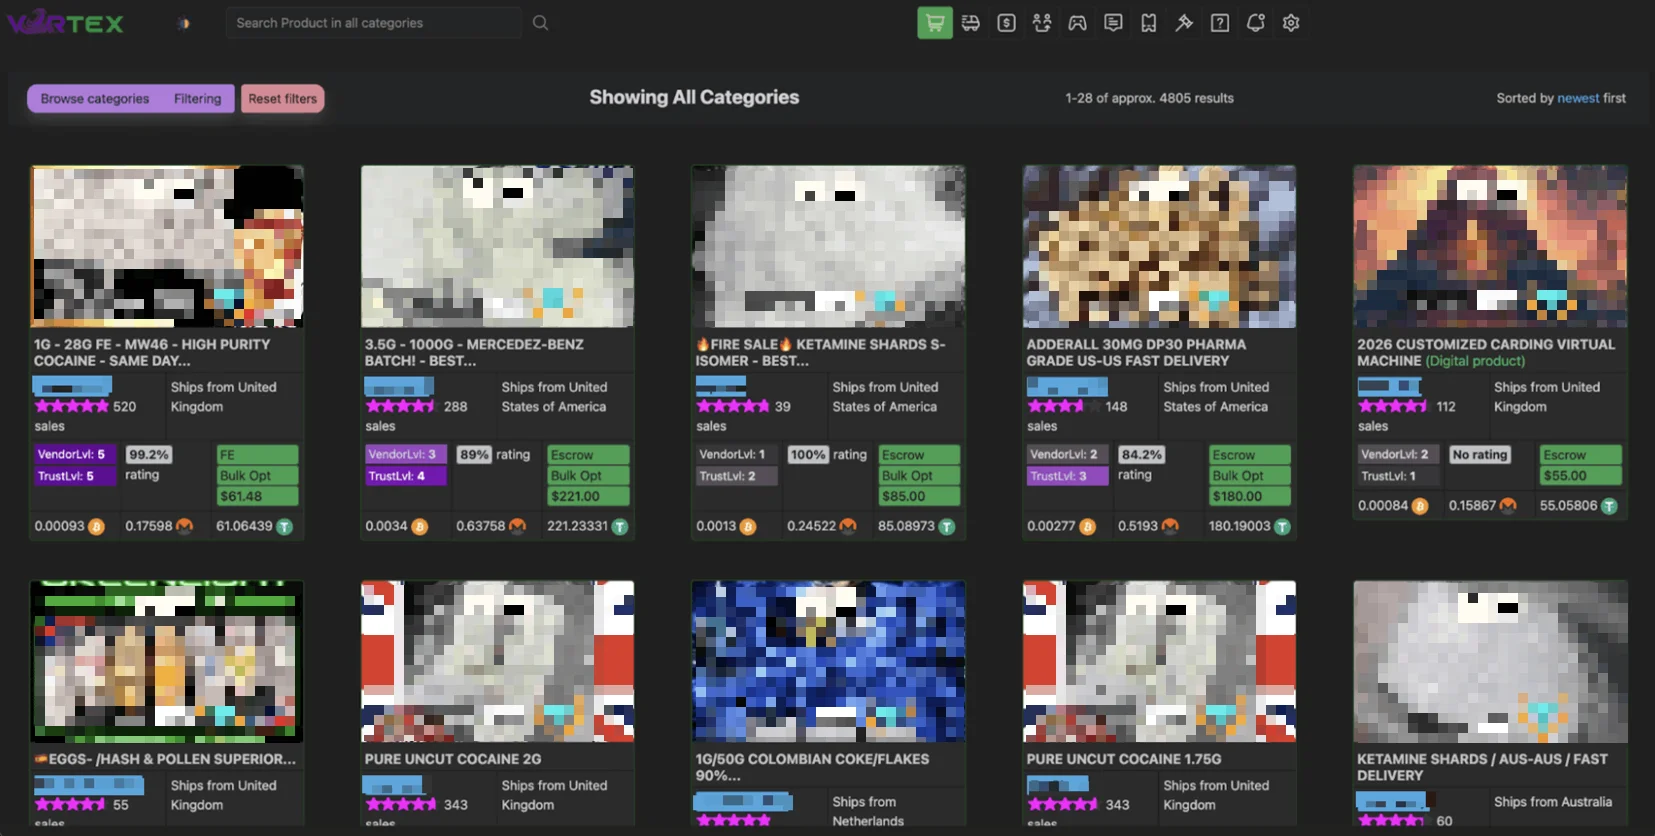
The cybersecurity landscape has changed significantly as digital payments, cloud computing, mobile applications, and online commerce have become part of everyday life. Unfortunately, cybercriminals have adapted alongside these developments. Modern cybercrime increasingly involves interconnected networks of criminals, stolen information, compromised accounts, malicious software, and underground communities.
Multi-purpose darknet marketplaces are one component of this ecosystem. These environments have been associated with various forms of illegal activity, including the circulation of stolen data, compromised credentials, and financial information. bclub is a name that has appeared in online discussions connected with underground payment-card activity.
Because illicit online services can change quickly, individual claims about bclub.tk or similar marketplaces should be treated carefully. Domains can become inactive, infrastructure can move, and unrelated operators can imitate established names. The broader cybersecurity trends, however, provide useful lessons for organizations and consumers.
What Are Multi-Purpose Darknet Marketplaces?
The term “darknet marketplace” generally refers to an online marketplace operating through infrastructure designed to provide greater anonymity than conventional websites.
Not all darknet services are illegal. Privacy-oriented networks can have legitimate applications in journalism, research, communication, and personal privacy.
The concern arises when particular services are used to facilitate criminal activity.
A multi-purpose marketplace may be associated with several categories of illicit activity rather than focusing on a single type of data or service. This can make the ecosystem more resilient because different criminal actors may interact within the same broader environment.
Bclub and Underground Payment-Card Discussions
Bclub has appeared in online discussions involving stolen payment-card information and underground marketplaces.
However, researchers need to distinguish between confirmed evidence and claims made by anonymous sources. Information about illicit services can be outdated or deliberately misleading.
A domain name can also be copied or impersonated. Consequently, the appearance of a name in online discussions does not automatically establish every claim made about it.
From a cybersecurity perspective, the more important subject is how payment-card information becomes compromised and why criminals attempt to circulate it through underground ecosystems.
How the Landscape Has Changed
Cybercrime has become increasingly interconnected.
In earlier periods, an individual attacker might have attempted to carry out an entire operation alone. Modern criminal ecosystems can involve specialization, with different actors focusing on different parts of an attack.
One group may attempt to compromise systems, another may obtain access, and another may provide infrastructure or financial services.
This specialization can make cybercrime more scalable while creating additional challenges for defenders.
The Growing Importance of Stolen Data
Stolen data remains a major cybersecurity concern because information can have value beyond the original attack.
Credentials, personal information, and payment details can potentially be combined with information from other sources.
This means a breach can create risks that persist after the affected organization has fixed the original vulnerability.
For consumers, this reinforces the importance of unique passwords, multifactor authentication, and regular account monitoring.
For businesses, it demonstrates why breach response should include assessing what information was exposed and what downstream risks may exist.
Phishing Remains a Major Entry Point
Despite the development of advanced cybersecurity technology, phishing continues to be an important method for obtaining sensitive information.
Attackers can imitate trusted brands, create convincing messages, and use urgency to pressure victims into making decisions without verification.
Organizations can reduce this risk through email security systems, multifactor authentication, employee training, and clear procedures for reporting suspicious communications.
Consumers should similarly be cautious about unexpected requests for passwords, payment information, or security codes.
Malware and Compromised Devices
Malware provides another route through which information can become compromised.
Malicious software can target computers, mobile devices, browsers, and other systems. Depending on the type of malware, it may attempt to steal credentials or other sensitive information.
Keeping software updated and using reputable security protections can reduce exposure to known threats.
Organizations should also monitor endpoints for unusual behavior and maintain appropriate security controls.
Why Financial Data Requires Special Protection
Payment information is particularly sensitive because it is directly connected to financial transactions.
A compromise can affect not only the individual cardholder but also merchants, payment processors, banks, and other organizations involved in the payment ecosystem.
Modern payment systems use multiple security mechanisms to reduce fraud, including transaction monitoring, authentication controls, automated analysis, and customer alerts.
These defenses demonstrate an important principle: cybersecurity is not dependent on a single security feature. Protection comes from multiple layers working together.
The Role of Cyber Threat Intelligence
Cyber threat intelligence helps organizations understand changing criminal activity.
Security teams can monitor reliable threat reports, investigate indicators of compromise, analyze attack patterns, and identify emerging risks.
Information about underground marketplaces may contribute to this work when it can be obtained and analyzed responsibly.
However, threat intelligence must be evaluated for reliability. Anonymous claims can be inaccurate, outdated, or deliberately deceptive.
Useful intelligence therefore requires context, corroboration, and careful analysis.
How Businesses Can Adapt
Businesses need to assume that the threat environment will continue changing.
A modern security program should include strong identity management, multifactor authentication, network monitoring, endpoint protection, vulnerability management, employee training, and tested incident-response procedures.
Data minimization is also valuable. Organizations should avoid retaining sensitive information longer than necessary and should restrict access to people and systems that genuinely require it.
Companies that handle payment-card information should also follow applicable industry standards and legal requirements.
Consumer Protection in a Changing Threat Environment
Consumers can take several simple steps to reduce their exposure.
Use unique passwords: Avoid using one password across multiple services.
Enable multifactor authentication: MFA can provide protection even when passwords are compromised.
Monitor accounts: Review financial transactions and respond promptly to unfamiliar activity.
Update devices: Security patches can address known vulnerabilities.
Verify messages independently: Do not rely solely on links or contact information contained in unexpected communications.
Secure email accounts: Protecting email is important because email-based password recovery can affect other accounts.
The Problem With Trusting Underground Marketplaces
Another important change in the underground ecosystem is the presence of scams within criminal communities themselves.
A website or forum associated with illegal activity may not provide what it claims to offer. Users of such services can also face phishing, malicious software, impersonation, and financial scams.
This demonstrates that underground environments should not be treated as reliable commercial services.
From a cybersecurity standpoint, avoiding interaction with illicit marketplaces eliminates a significant source of unnecessary security and legal risk.
Artificial Intelligence and Automation
Artificial intelligence is becoming increasingly relevant to cybersecurity.
Defenders can use automation and AI-assisted systems to process large amounts of threat information, identify suspicious patterns, and prioritize security alerts.
Attackers may also use automation to increase the volume of phishing attempts or generate convincing fraudulent communications.
This does not make human awareness less important. Instead, it makes the combination of technical controls and informed users increasingly valuable.
The Importance of Responsible Research
Security researchers studying darknet marketplaces must balance the value of intelligence with ethical and legal considerations.
Responsible research should protect victims, avoid unnecessary exposure of sensitive information, and refrain from facilitating criminal activity.
Researchers should also carefully document the limitations of their findings.
When examining Bclub-related claims, this means distinguishing verified evidence from speculation and recognizing that underground infrastructure can change quickly.
What the Future May Look Like
The future of underground cybercrime is likely to involve greater specialization, automation, and integration between different criminal services.
At the same time, defenders are developing better fraud detection, authentication technologies, threat intelligence, and automated security monitoring.
This creates a continuous cycle of adaptation.
As criminals change their methods, security professionals must identify emerging patterns and strengthen defensive controls.
Conclusion
The changing landscape of multi-purpose darknet marketplaces illustrates how cybercrime continues to adapt to new technologies and digital business models. Bclub has appeared in online discussions related to underground payment-card activity, but specific claims about illicit services require careful verification because domains and infrastructure can change or be impersonated.
The broader lesson is that underground markets are connected to a much larger ecosystem involving phishing, malware, data breaches, compromised accounts, social engineering, and financial fraud.
Consumers can reduce their risk through unique passwords, multifactor authentication, transaction monitoring, software updates, and cautious handling of unexpected messages.
Businesses need layered defenses that include access controls, security monitoring, employee education, data minimization, vulnerability management, and effective incident response.
Cyber threat intelligence can help organizations understand emerging risks, but it must be based on reliable evidence and responsible research practices.
Ultimately, studying underground marketplaces is most valuable when the knowledge gained is used to strengthen cybersecurity. Understanding how threats evolve allows individuals, businesses, financial institutions, and security professionals to prepare for new risks and protect sensitive information in an increasingly connected digital world.